GitHub Package Firewall vs. StepSecurity Secure Registry: Protection beyond npm
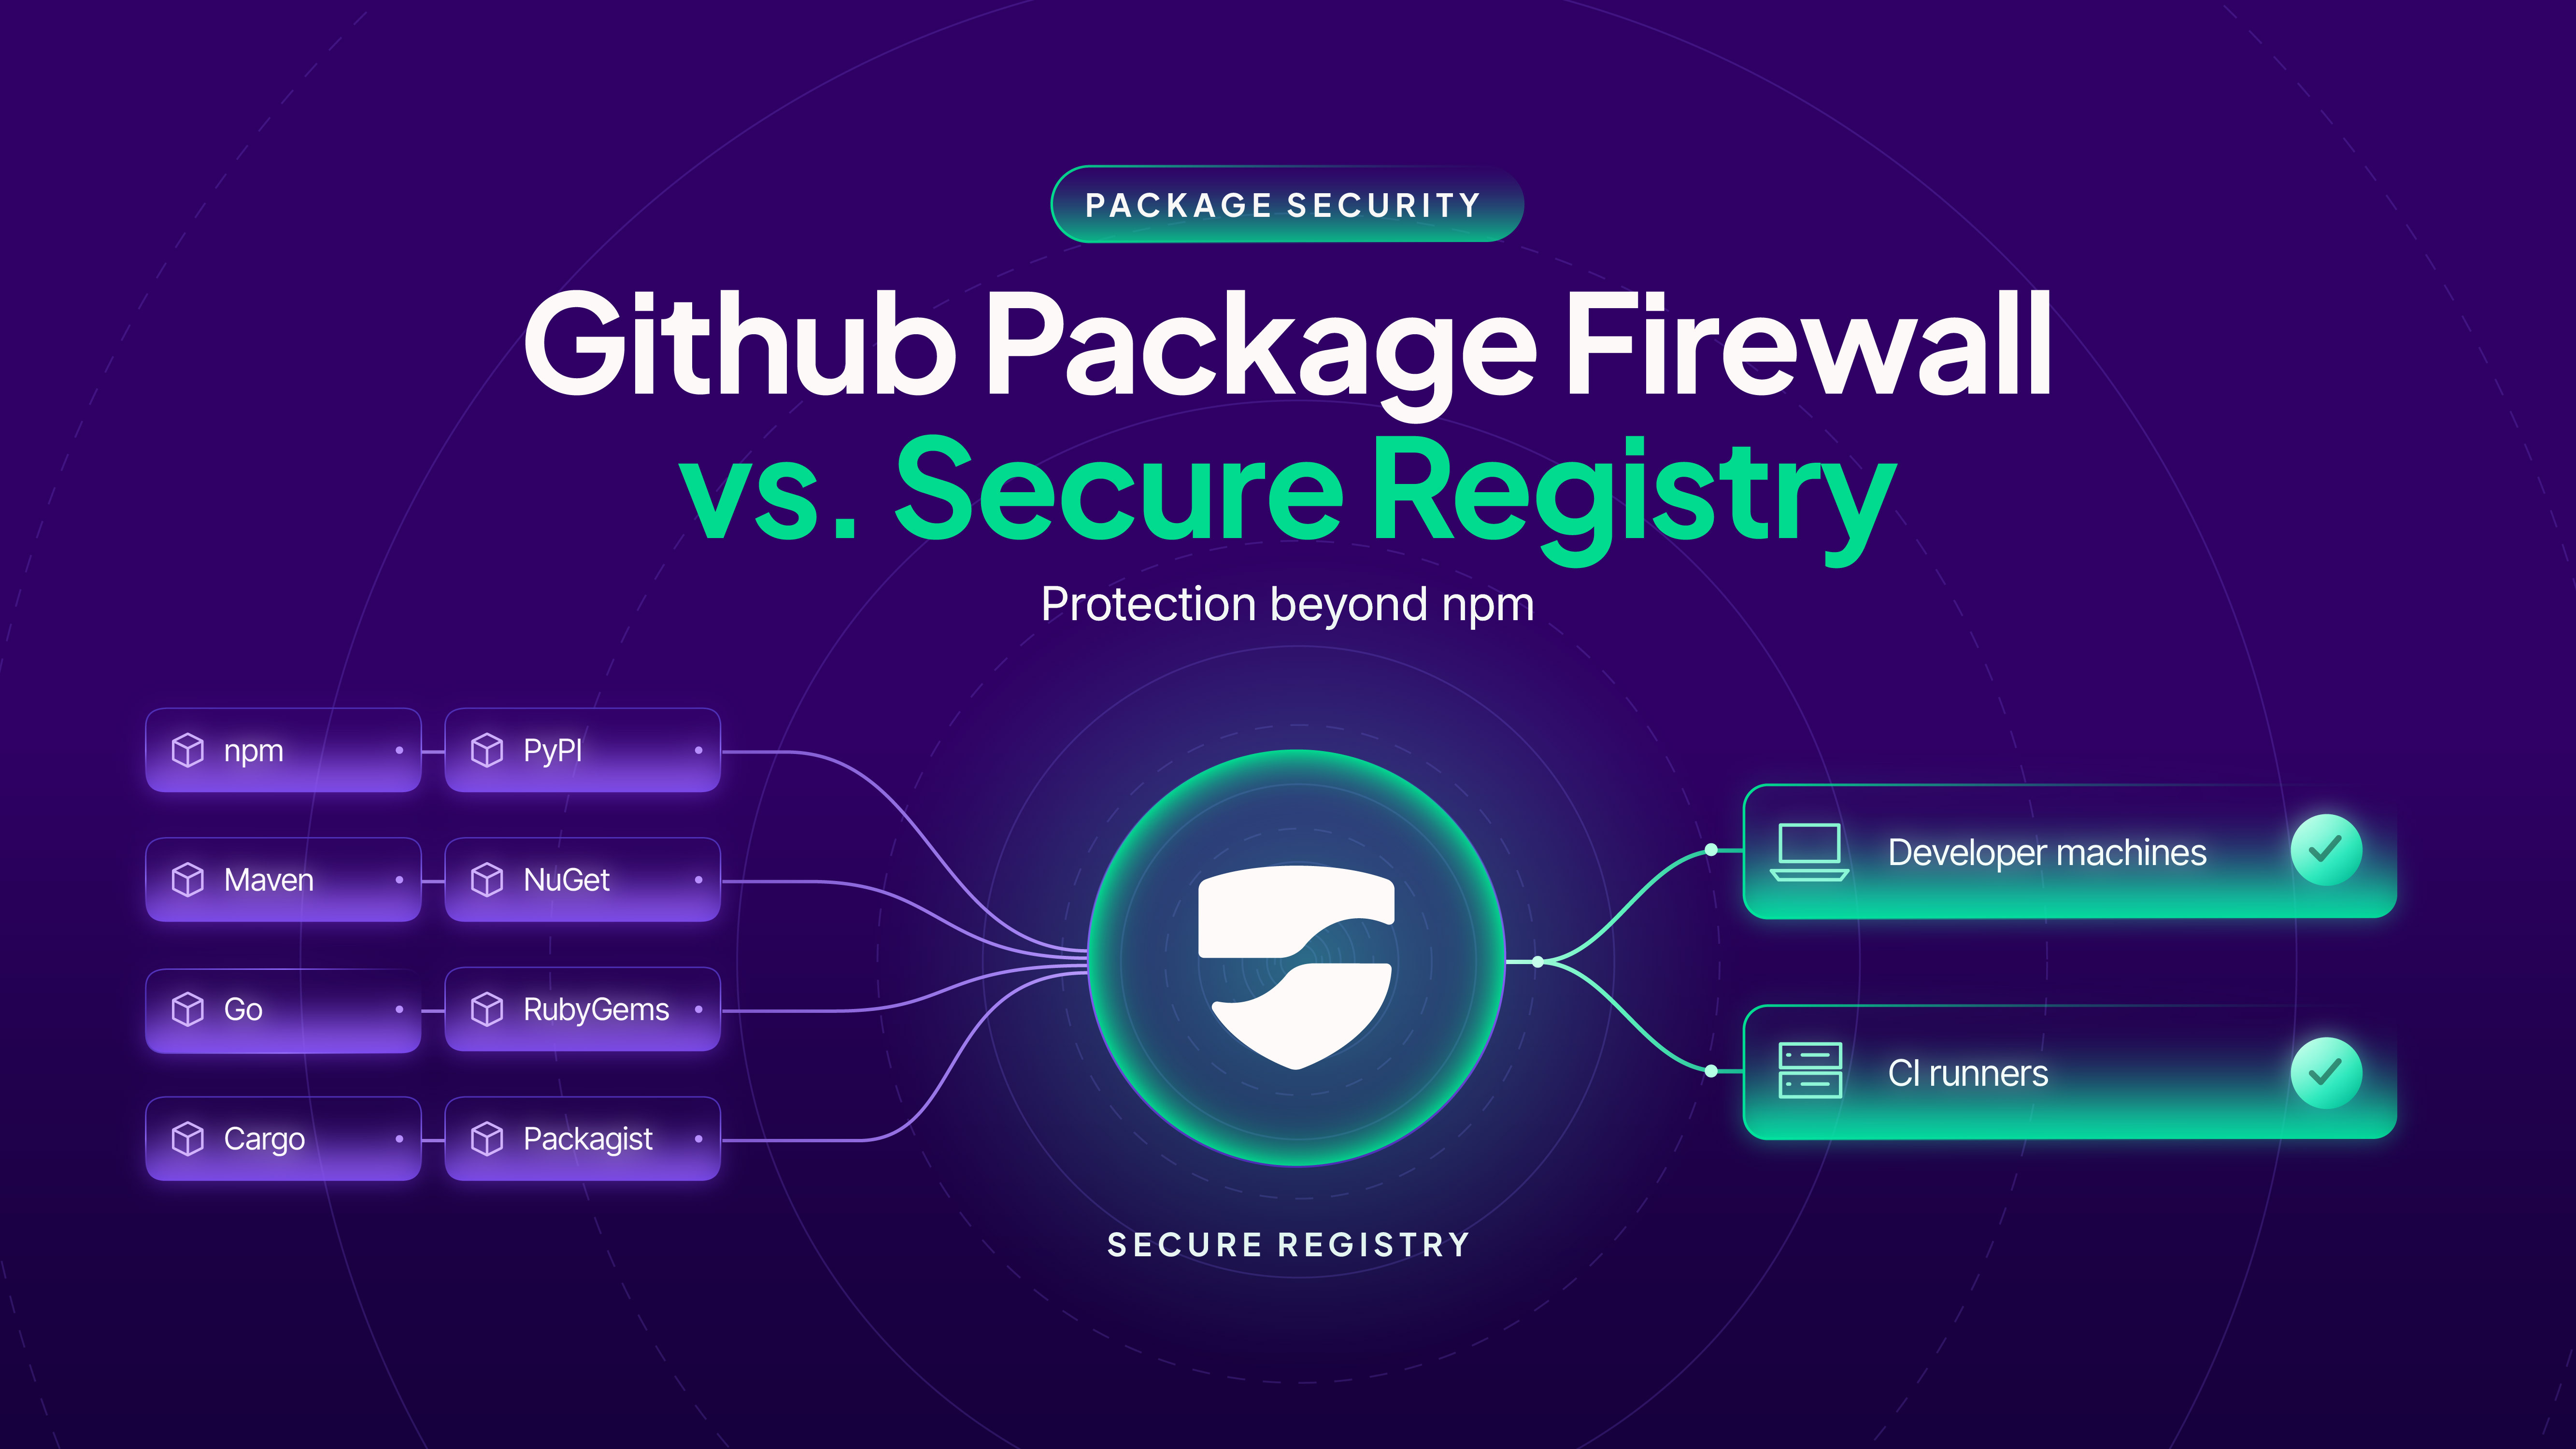
GitHub’s package firewall covers npm only. StepSecurity's Secure Registry protects 8 ecosystems, traces every install, and blocks malicious packages within an hour
March 2025
Application Security
Learn how StepSecurity Harden-Runner detected the tj-actions/changed-files supply chain attack
January 2024
Researchers detail a CI/CD attack leading to PyTorch releases compromise via GitHub Actions self-hosted runners
Sept 25, 2024
Stripe Repository Breach
The Vulnerability in Stripe’s GitHub Actions Workflow Shows Why Securing CI/CD Pipelines Is Essential
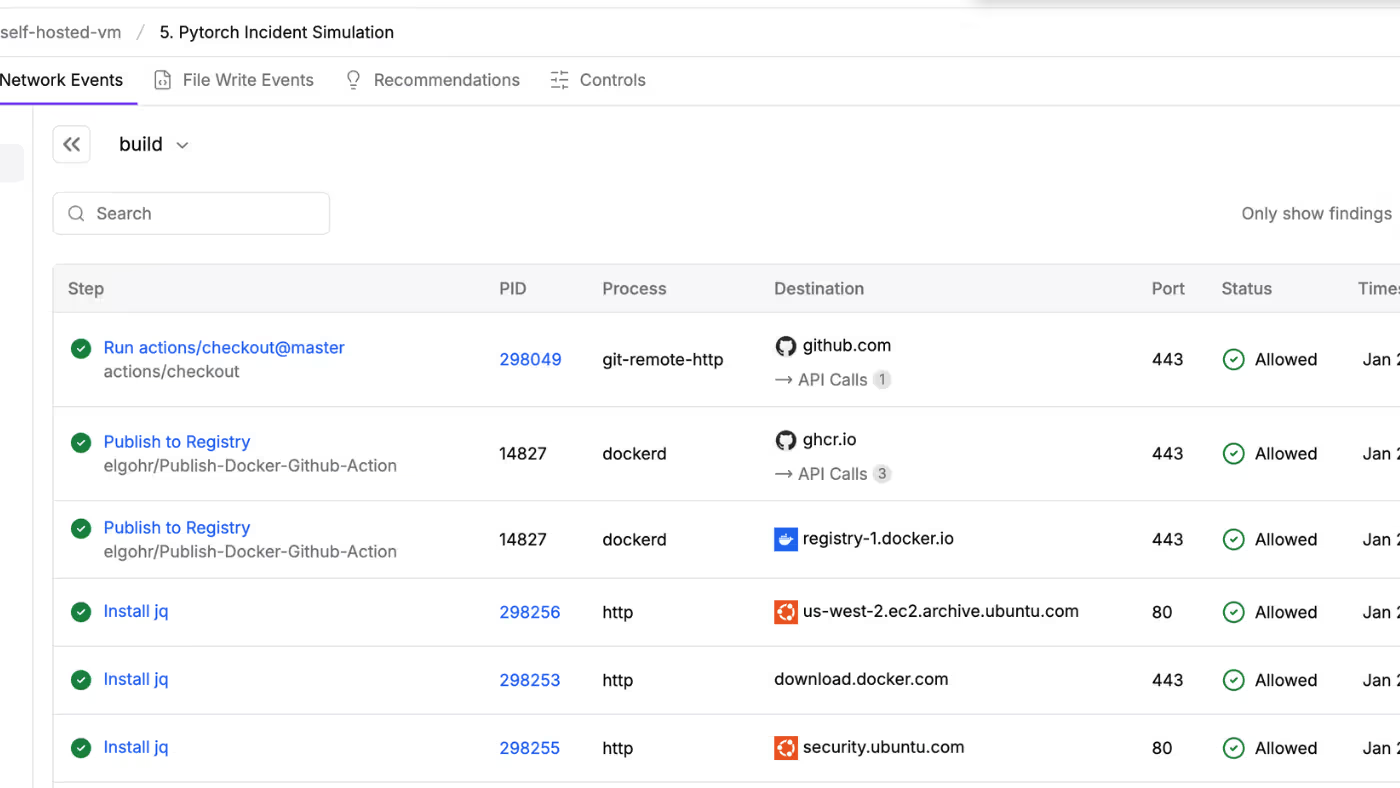
Harden-Runner monitors network, file, and process activity on CI/CD runners—blocking suspicious behavior instantly. Proven in the wild: it caught the tj-actions/changed-files breach.
01
Gain full visibility into which job step initiated each network call, file write, or process execution.

02
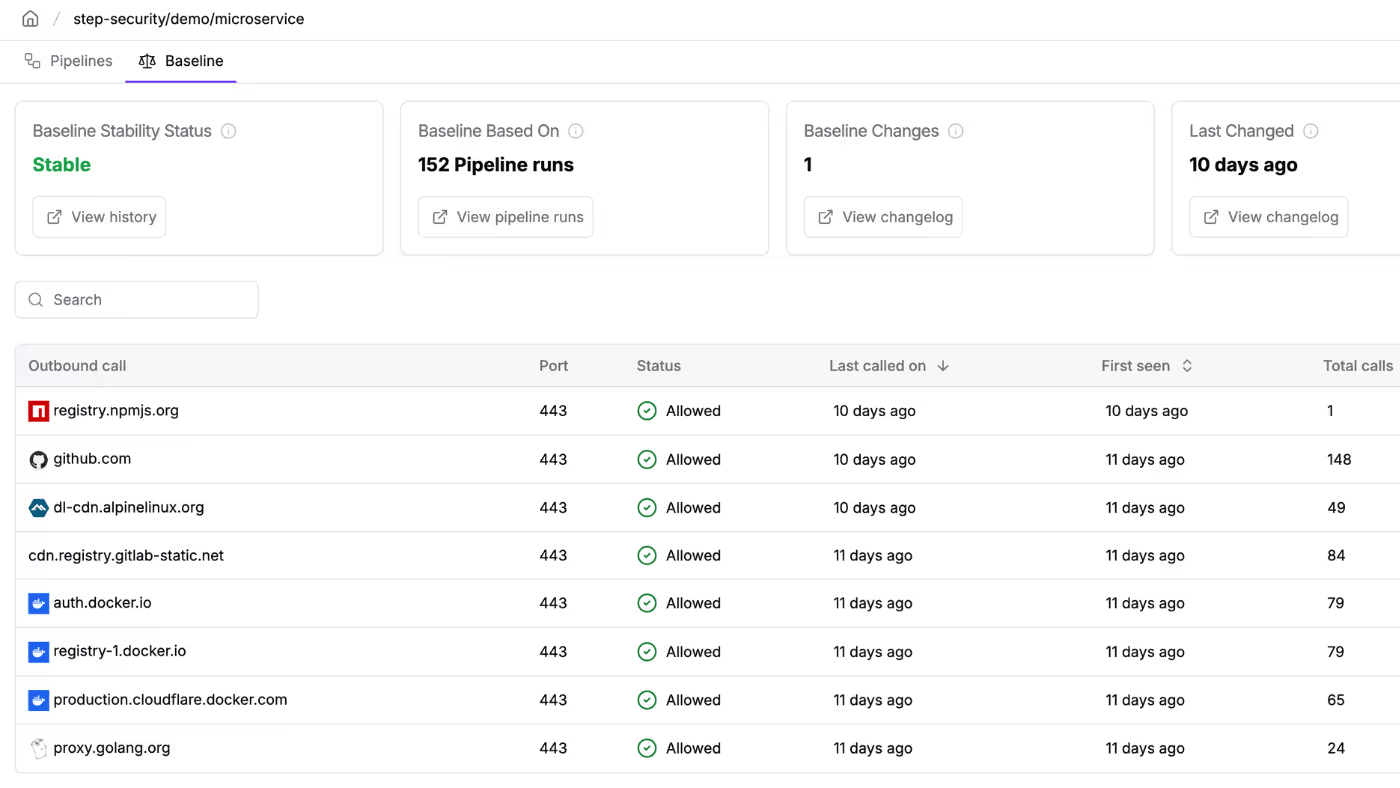
Automatically baseline network behavior for every job in your CI/CD pipeline.

03
Get alerted when a job makes a network call outside its normal behavior. How the tj-actions breach was detected!
04
Only allow what’s needed. Block unauthorized network traffic using job-level baselines.
05
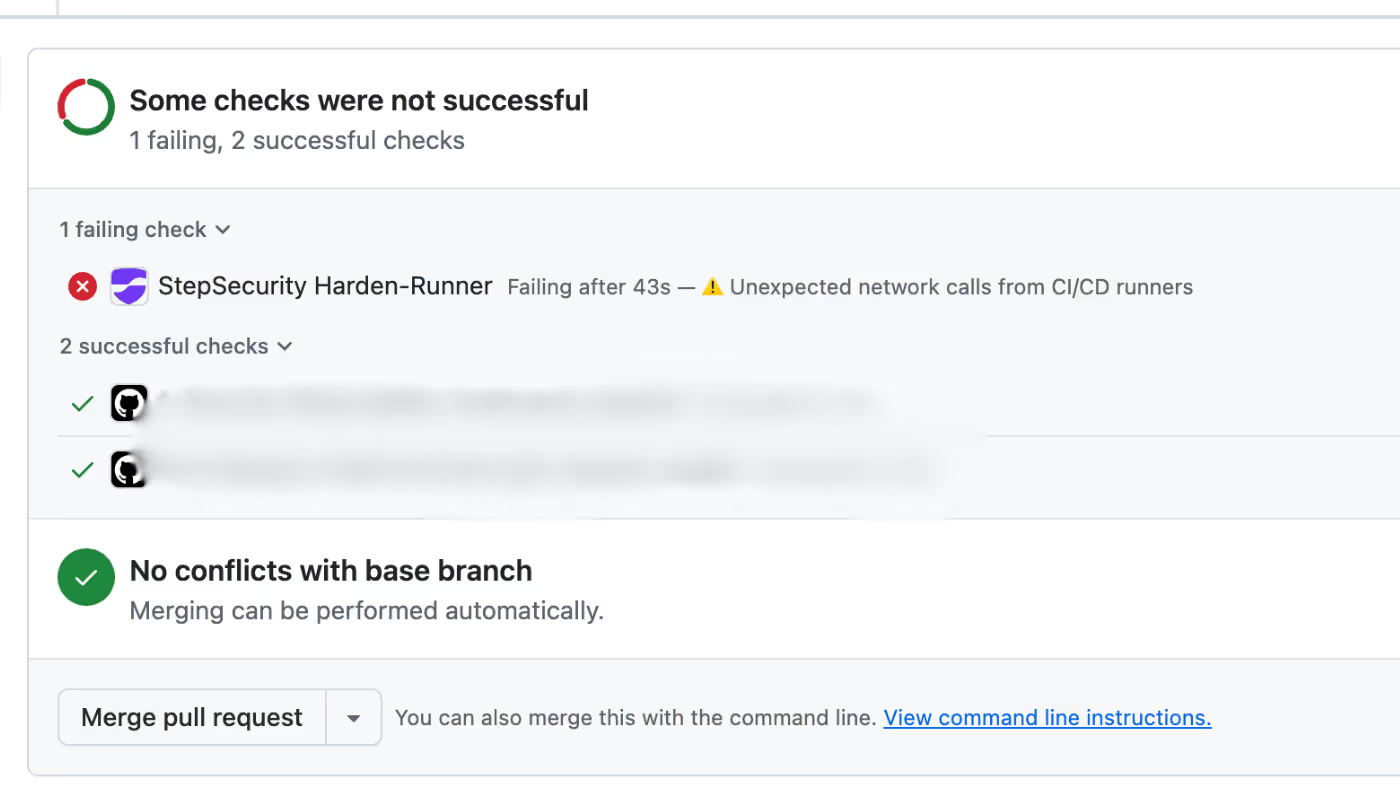
Get real-time security feedback right where you work.

StepSecurity empowers organizations to vet, approve, and manage Actions internally—ensuring developers move fast while staying compliant with enterprise-grade security policies.
01
StepSecurity Maintained Actions are drop-in replacements for third-party Actions—hardened, verified, and actively maintained.
02
Track every Action used across repositories to identify risks and enforce best practices.

03
StepSecurity assigns a security score to third-party GitHub Actions—helping you choose safe, vetted options for your workflows.
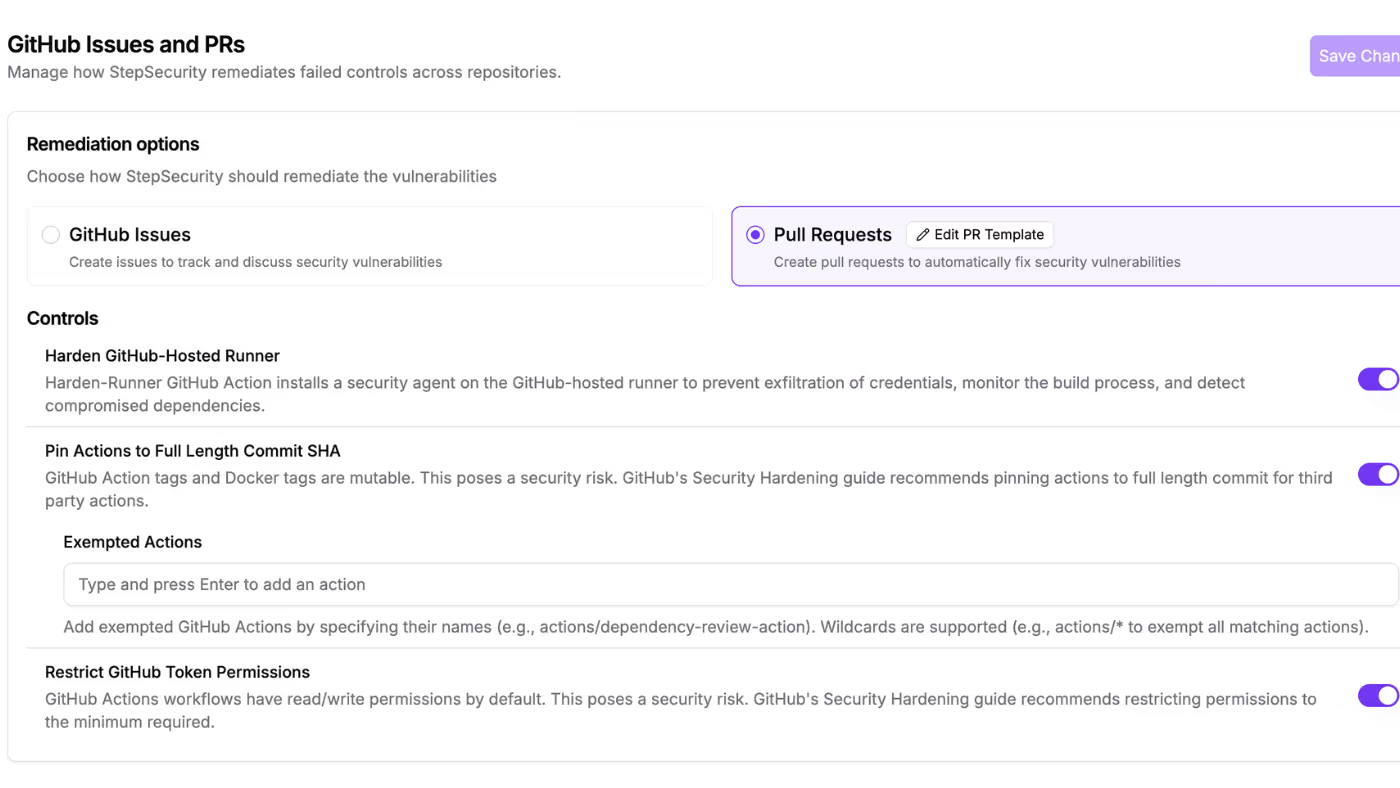
Instead of manually editing workflows or writing new YAML from scratch, StepSecurity lets you apply consistent, automated best practices with ease.
01
Automatically create pull requests to bring your workflows in line with best practices.
02
Pin third-party actions to commit SHAs with automated pull requests for tamper-proof CI/CD.

03
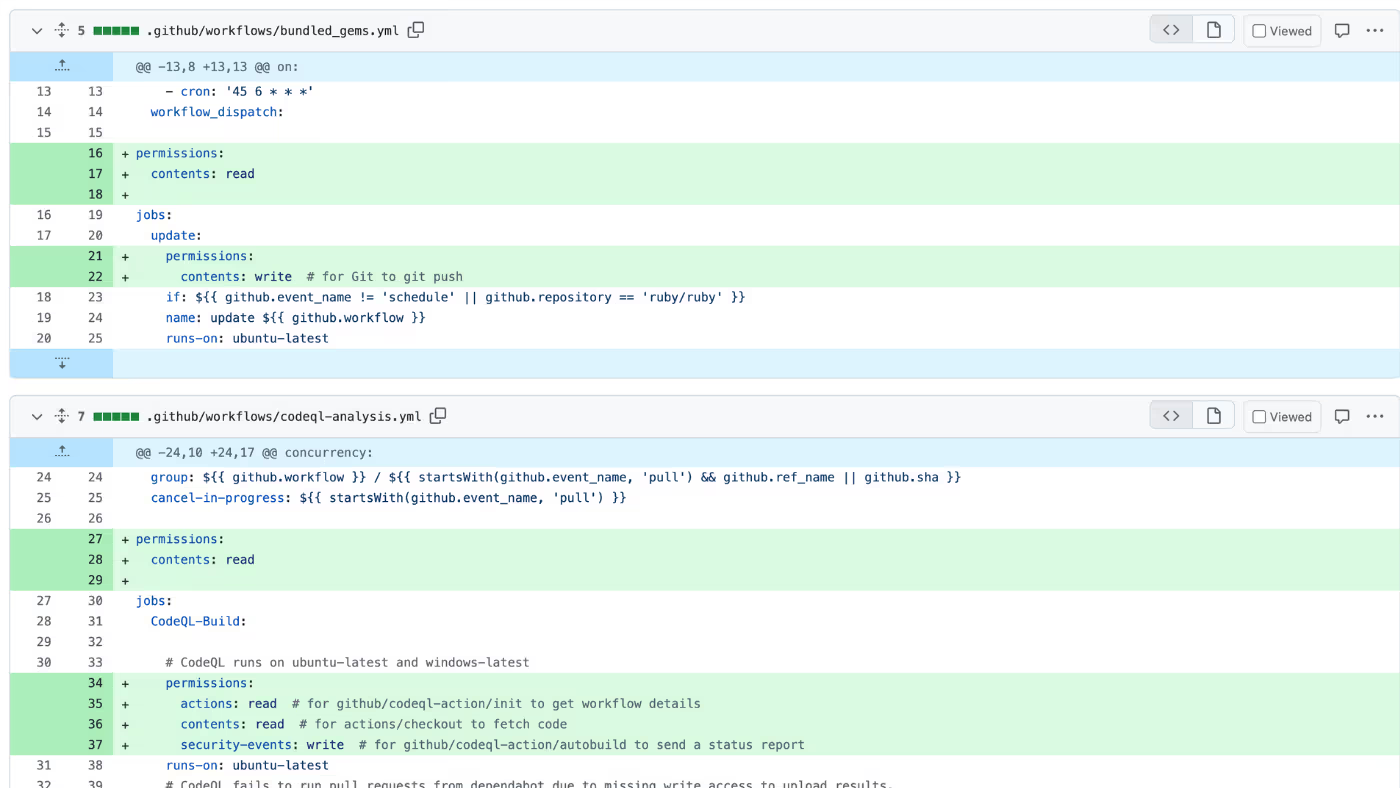
Automatically set minimal GitHub token permissions with secure pull requests.

04
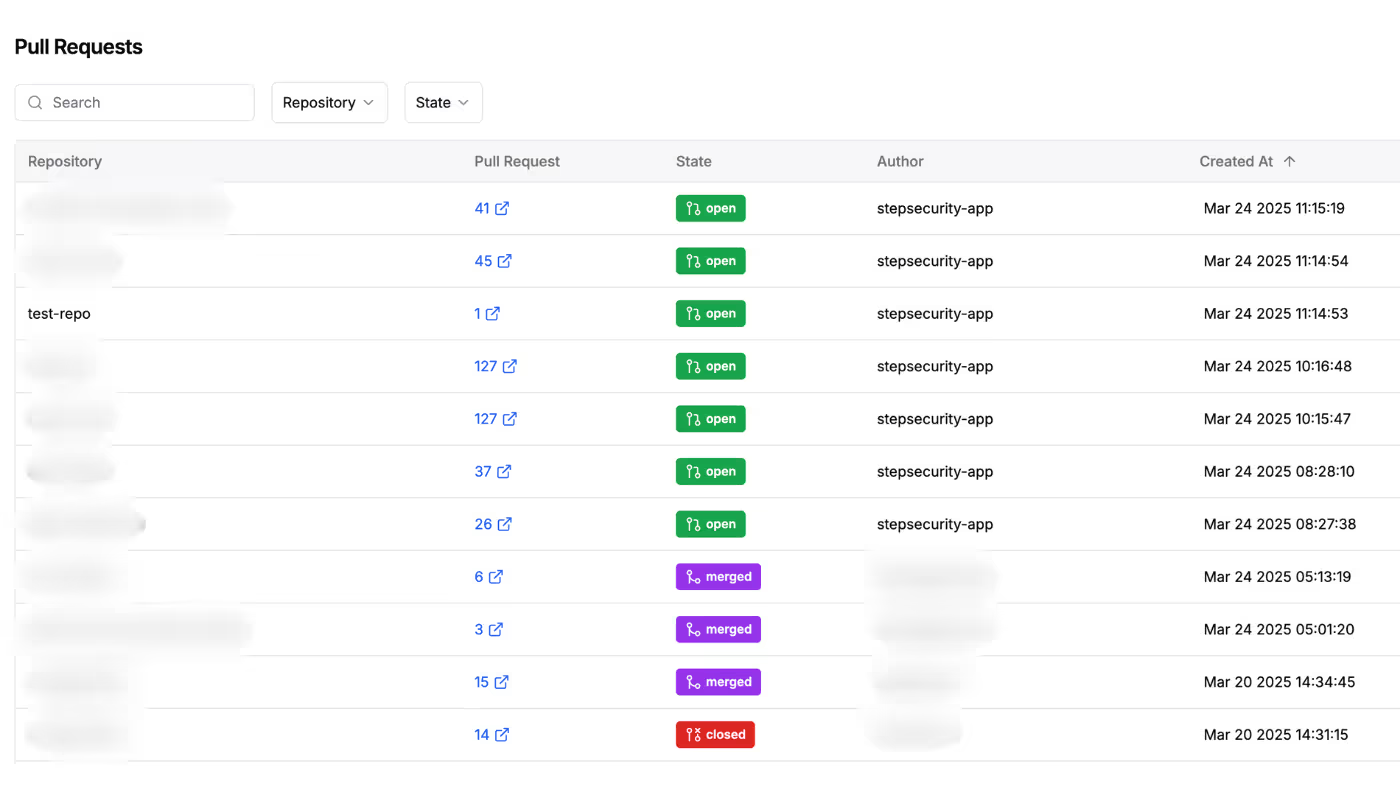
Monitor and manage all automated pull requests from StepSecurity in one centralized view.

Experience the StepSecurity Difference

GitHub’s package firewall covers npm only. StepSecurity's Secure Registry protects 8 ecosystems, traces every install, and blocks malicious packages within an hour

Binance says its $6.34 billion theft began when an engineer ran a fake interview assignment on his work computer. JFrog has now exposed a fake company, AccuraSoftHire, built to run the same trick. We decoded the attacker's server history from a public Ethereum wallet and found npm packages from the interview task that stayed installable for up to seven months. Here is what to check on your developer machines.